Most of them aren't. 360 is the Buffalo cybersecurity company for firms of 10 to 50 people that have to meet HIPAA, GLBA, PCI or NIST. We lock your systems down, close the compliance gaps and keep the paperwork ready for when someone asks.
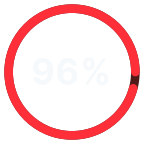
OF RANSOMWARE VICTIMS WERE
Most attacks aren't aimed at anyone in particular. Attackers hunt for stolen passwords and unpatched equipment, then hit whoever has them. One missing policy, one unencrypted laptop or one untrained employee is enough.
Source: Verizon 2026 Data Breach Investigations Report (organizations under 1,000 employees, where size was known)

COMPLIANCE FRAMEWORKS WE COVER

HIPAA

GLBA

PCI DSS

NIST

CMMC

SOC 2
Readiness
From gap assessments to ongoing monitoring, we build and maintain the security and compliance work that keeps you protected, ready for an audit and in business.

We close the gaps and build the documentation an auditor or insurer asks for, so you're not scrambling when the letter arrives.

We watch your network and devices 24/7 and respond to suspicious activity before it becomes a breach.

Security, compliance and your everyday IT sit with one local team, so nothing falls between vendors.

Find the gaps before an auditor, insurer or regulator does.
Identify Gaps

Written policies that match how your office actually works.
Build. Document. Comply.

IT compliance all year, not only the week before an audit.
Monitor 24/7

The risk analysis HIPAA requires, done and documented.
Reduce Risk

Phishing tests and short training your staff will actually finish.
Train. Educate. Protect.

A written plan for the day something gets through, so you're back up and running fast.
Be Prepared

We monitor your network and devices 24/7 to catch threats early.

We rank your risks by what they would cost the business.

We put the controls in place: MFA, encryption, patching and backups.

We keep watching and adjust as threats change.

You get clear reports you can hand to an auditor or insurer.
Free Technology Assessment (30 Minutes)

Your complete technology partner. Built for businesses that can't afford to slow down.
Proudly serving Amherst, NY and Western New York.


